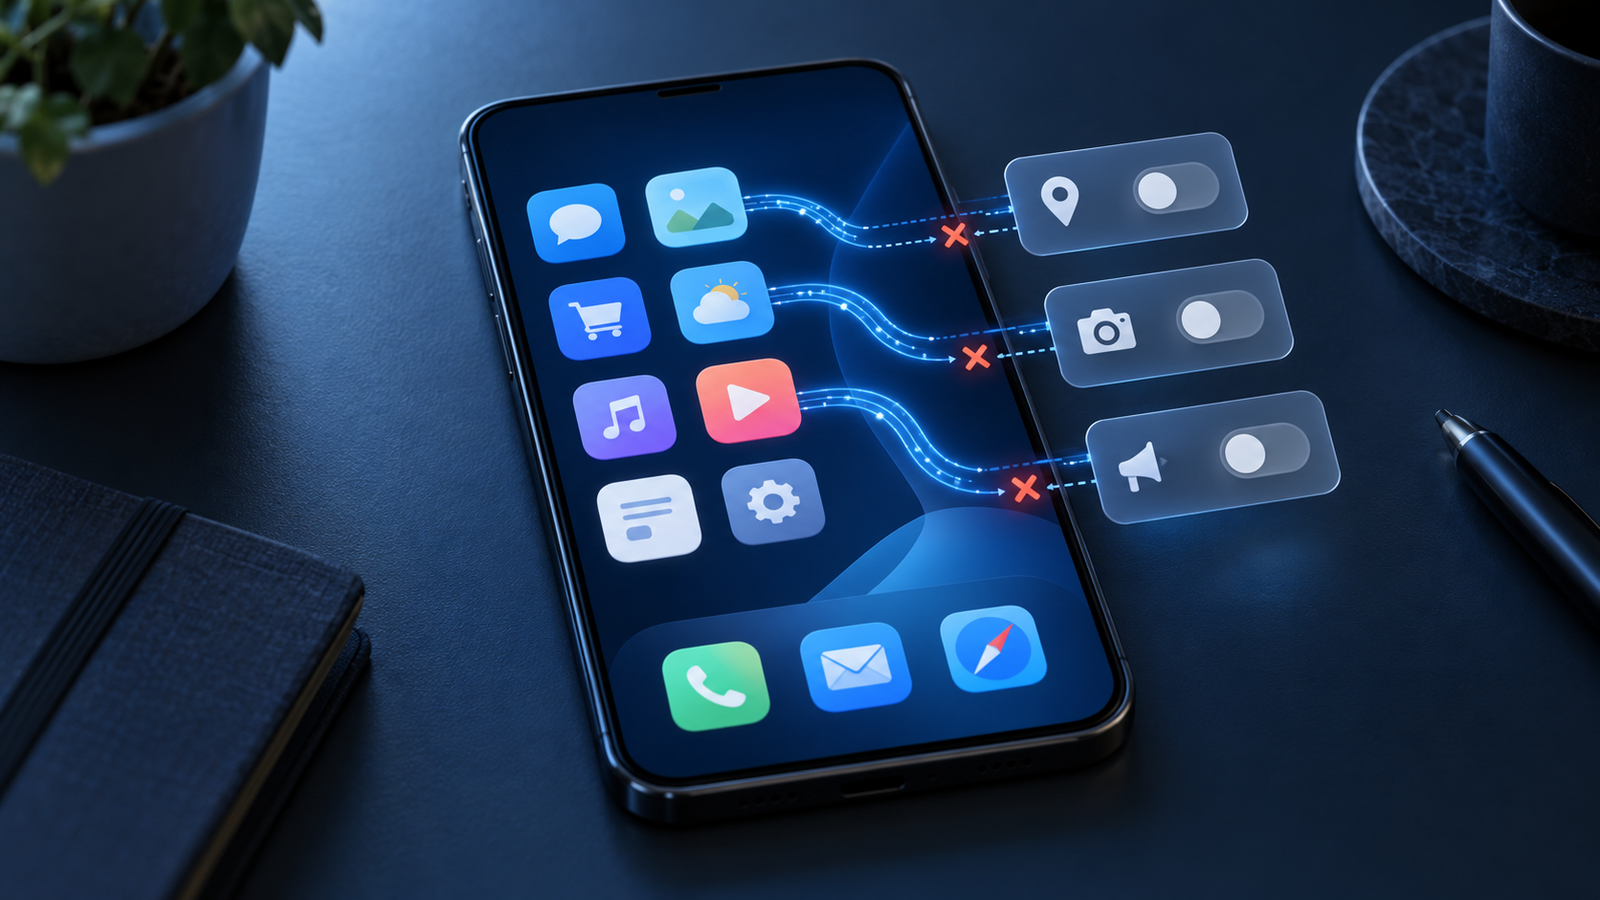
To reduce app tracking, separate the information an app uses from the controls available on your phone. Advertising identifiers, cross-company tracking permission, location access and data you type into an account are different things. Turning off one mechanism does not automatically disable all the others.
Start with a small review of the apps you actually use. The steps below refer to Android and iPhone controls documented by their platform vendors; labels and available options vary by device, operating-system version and account. On a managed phone, follow the organization’s policy rather than trying to override it.
Start with the apps and the task
List apps you use regularly, apps you rarely open and apps you do not recognize. For each regular app, describe the feature you need and the information that feature reasonably requires. A navigation task and a reading app need different access, so avoid treating every permission request as equally necessary.
Remove apps you no longer need using the supported system process, but first check whether they contain unsaved local work or an account you still depend on. Uninstalling an app is not the same as deleting its server-side account or requesting removal of previously collected information.
Keep the review manageable: change one app or permission group, test the intended feature and note what changed. If a feature stops working, investigate its documented requirement before restoring every permission. The aim is a deliberate, understandable boundary rather than a phone that is difficult to use.
Review iPhone tracking requests
Apple’s App Tracking Transparency guidance concerns linking activity across other companies’ apps and websites for advertising or sharing with data brokers. In Settings, Privacy & Security, then Tracking, review the listed apps and the option to allow apps to request tracking.
Apple says choosing Ask App Not to Track prevents access to the system advertising identifier and does not permit the developer to substitute other identifying information for that tracking purpose. This is a defined platform permission and policy boundary. It does not mean the app can no longer process your sign-in, purchases or information you deliberately provide for its service.
Read an app’s explanation without assuming the feature requires advertising tracking. Review existing choices as well as future prompts. If the tracking control is unavailable, consult Apple’s documented account and management restrictions rather than attempting an unsupported workaround.
Review Android advertising controls
Google documents Android’s ad privacy settings, including ad topics, app-suggested ads and ad measurement. On supported devices, its current route is Settings, Google, All services, then Ads under Privacy & security, followed by Ads privacy. Use Settings search or manufacturer help if your device differs.
Review each available control rather than assuming a single setting governs every advertising mechanism. Google distinguishes these features from advertising ID settings and individual app policies. Opting out of a supported feature changes that feature; it does not promise an ad-free experience or erase every piece of information an app holds.
Treat advertising preferences and ordinary app permissions as separate reviews. A change to ad topics does not answer whether an app can access location, and denying location does not prevent an account-based service from seeing actions performed inside that account. Record what a control actually changes.
Limit device permissions to the feature
On Android, Google documents app permissions under Settings, Apps, the selected app and Permissions. You can also inspect a permission type across apps. Depending on the permission and system, options may include access while using the app, asking each time or denying access.
On iPhone, Apple’s privacy and Location Services guidance describes reviewing access categories in Settings, Privacy & Security. Check camera, microphone, contacts, photos and other relevant categories. An app normally appears in a permission list after requesting that access; an absent entry is not a complete account of its data practices.
Choose the narrowest supported option that serves the feature. A temporary camera task does not necessarily require ongoing access to the full photo library. Check the actual choices offered and test the result. Avoid granting broad access merely because a prompt appeared before you understood the feature.
Give location its own review
Android’s location-permission guide distinguishes when an app may access location and, where supported, precise versus approximate access. Review background access carefully and choose precision based on the task. Follow the equivalent Location Services options documented for your iPhone version.
A location permission is not the only way a service can receive contextual information. An address you type or information already associated with an account remains a separate data source. Do not interpret an approximate-location choice as a guarantee that a service cannot infer anything about where you are.
| Control | Question it helps answer | What it does not prove |
|---|---|---|
| Tracking permission | May cross-company tracking occur? | No account data is processed |
| Location permission | When and how precise is access? | No other location clues exist |
| Camera/microphone access | May this feature use the sensor? | No other data is collected |
| Privacy activity report | What supported activity was recorded? | Every connection is tracking |
Use activity reports as evidence, not verdicts
Android’s privacy dashboard shows supported permission access and allows you to review the apps involved. Its availability and history depend on the system version. Use it to investigate an unexpected access, not as a complete record of every data transfer or a guarantee that nothing happened outside its scope.
Apple’s App Privacy Report can show supported sensor and data access alongside contacted domains. It begins gathering information only after you enable it. A blank report immediately afterward does not establish that an app has never accessed data.
A contacted domain is a lead for investigation, not proof of wrongdoing. It may support content or an expected service. Compare the access with what you were doing, the app’s explanation and its privacy documentation. If the purpose remains unclear, reduce access or stop using the app rather than inventing certainty from a domain name.
Read disclosures with the right expectations
Google Play’s Data safety section lets developers describe collection, sharing and security practices. Google explains that disclosure categories have specific definitions and exceptions. Treat the section as developer-provided information to read alongside the privacy policy and your experience, rather than an independent audit.
Ask what is required for the feature, what is optional, who receives information and what retention or deletion process is described. When a policy is unclear, ask the developer or choose an alternative with a more understandable data relationship. A high rating or familiar icon does not resolve those questions.
Privacy limit Phone controls can reduce specific permissions and tracking mechanisms. They cannot promise complete anonymity, delete every previous server-side record or verify an app’s entire behavior. Use several understandable controls instead of relying on one switch.
Keep a short, repeatable phone review
For a fictional weather app, a useful review might begin by testing a manually chosen city instead of automatically granting background precise location. Whether that option exists depends on the app. The point is to match access to the feature, not to assume every weather app has identical requirements or practices.
- Identify necessary apps and preserve any important local data.
- Review supported advertising and tracking controls.
- Reduce unnecessary sensor, contact, photo and background-location grants.
- Use privacy reports to investigate specific unexpected access.
- Read the developer’s data and deletion explanations.
- Repeat the review after new apps or major workflow changes.
Reducing app tracking is an ongoing set of bounded decisions. Keep the apps and access that serve a clear purpose, question unexplained requests and understand what your platform can enforce or report. That approach gives you practical control without promising that a phone can become invisible to every service it uses.